Infinite Expansion · Records & Compliance
Built for businesses that can't afford to lose a record.
The tools to answer a request are already there.
Sensitive data is encrypted. Every view, change and deletion is audited. When a records request, a lawsuit or a privacy request arrives, you can search everything, place a legal hold, collect and export, and keep the log regulators expect.
Built for HIPAA, GDPR and records-retention workflows.
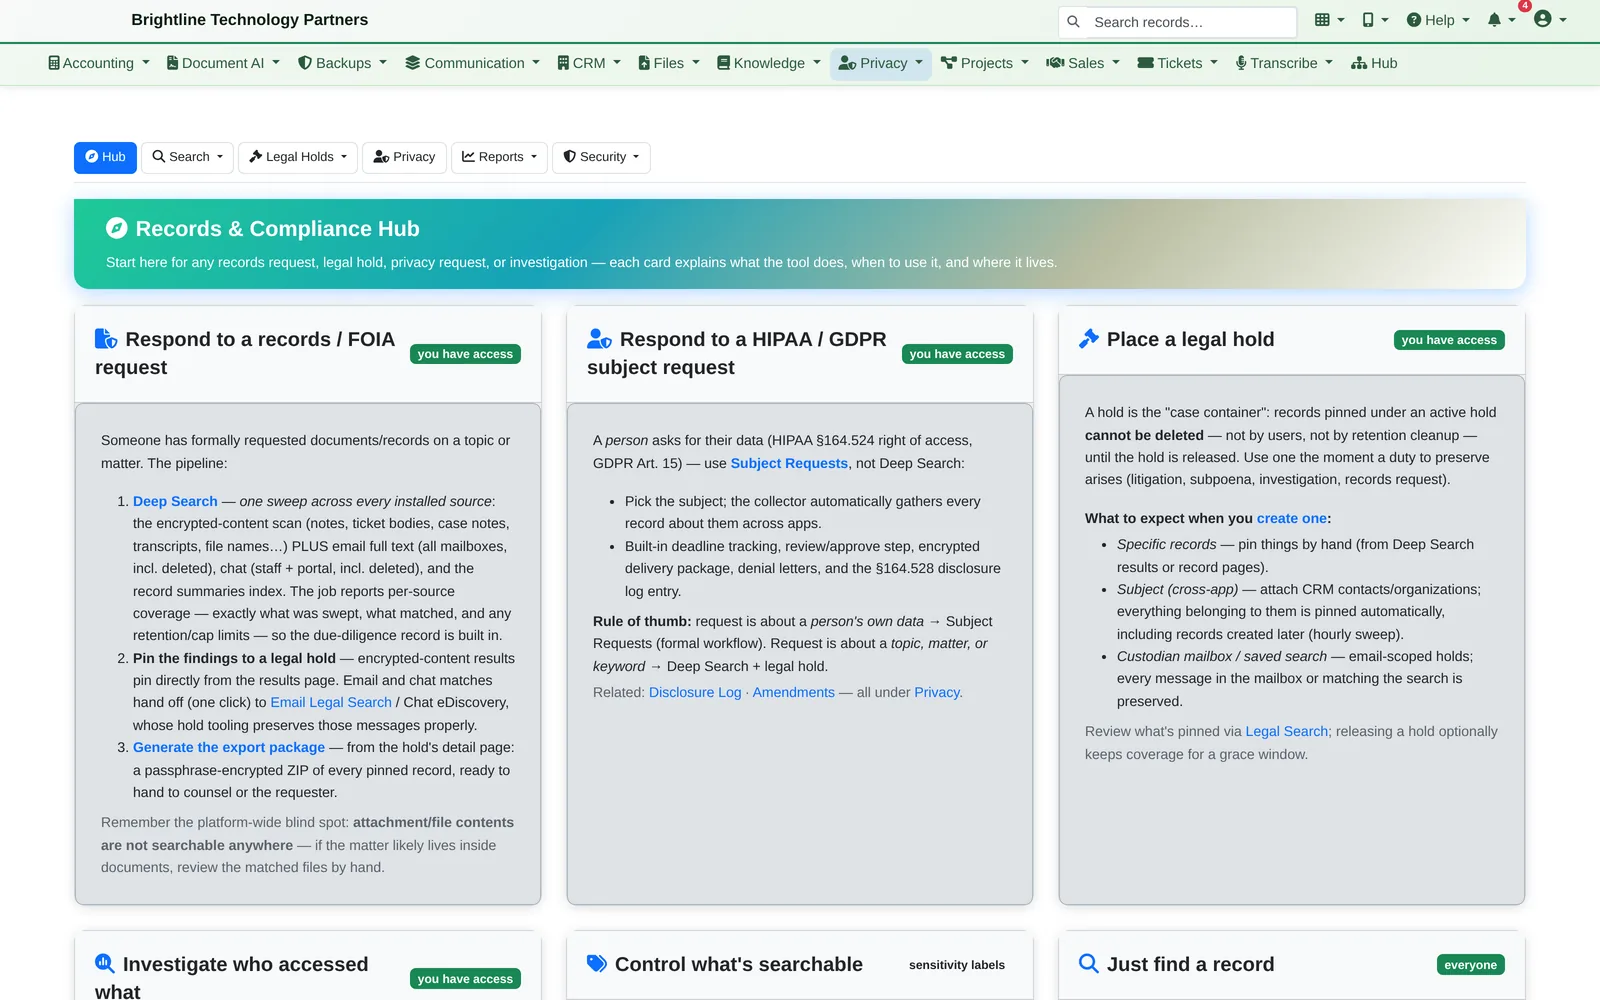
One hub for every kind of request. Each card explains what the tool does, when to use it and where it lives, so the person answering doesn't have to be an expert.
A Records Request Arrives
Search everything, hold it, hand it over.
- Search everything at once: emails, notes, tickets, chat, meeting transcripts and file names, with a written record of exactly what was searched.
- Place a legal hold. Records under an active hold can't be deleted, by users or by retention cleanup, until it's released, and nobody's work is disrupted. Holds can follow a contact or organization, so records created later are held too.
- Collect and export everything pinned to the hold as one encrypted package, ready for counsel or the requester.
Privacy and Individual Rights
When a person asks for their own data.
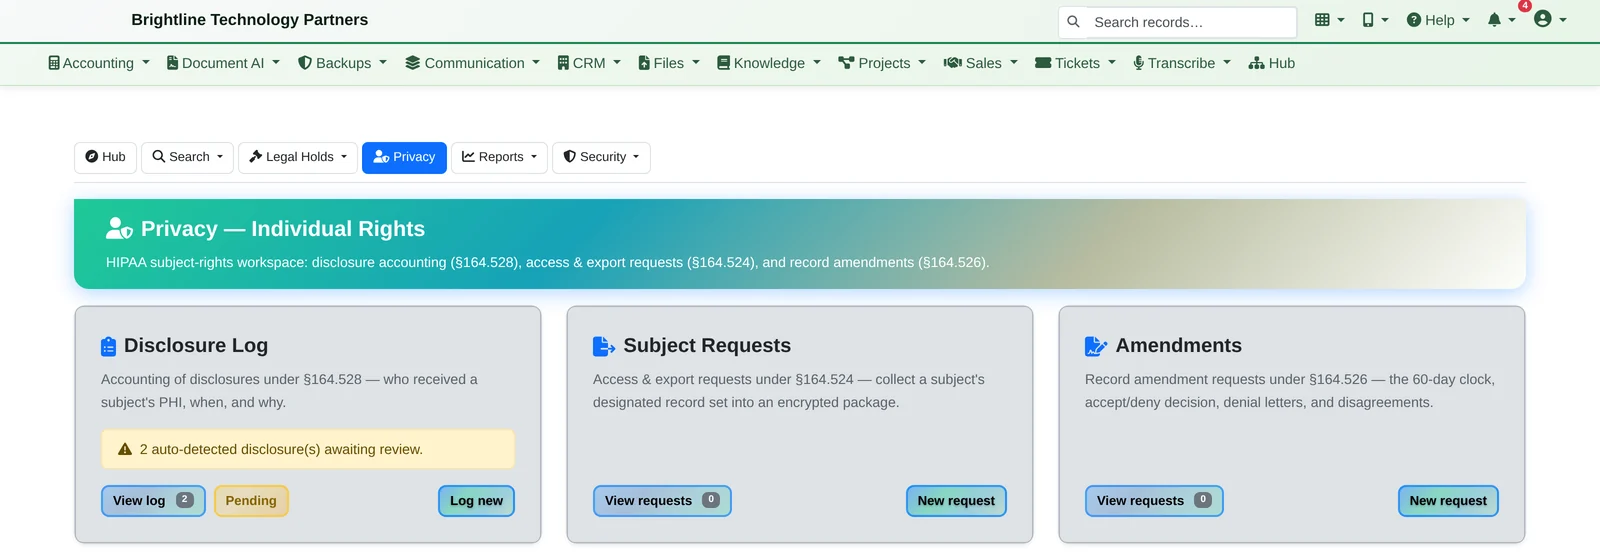
Disclosure log
Who received a person's information, when and why, with possible disclosures flagged for review.
Access and export requests
Gather the person's records from every app into an encrypted package, with deadline tracking and a review step before it goes out.
Amendment requests
Requests to correct a record, with the deadline clock, the accept or deny decision and denial letters.
Security Underneath
Encrypted, audited and locked down by default.
Encryption
- Sensitive fields, documents and stored email, with managed key rotation
- Encrypted off-site backups
- Sensitivity labels to control what's searchable
Audit trail
- Who viewed what, with field-level change history
- Deleted-record history
- Breach-detection alerts and a security-event (SIEM) feed
Access
- Two layers of access control: by organization and team, and by app role
- Multi-factor sign-in with an authenticator app, email or Duo
- IP restrictions, session controls and single sign-on
Compliance Programs
Your compliance program, in the same system.
Recurring control checks, assessments and document management, next to the records they're about.
Running servers too? Secure Server Access records every session and maps its evidence to SOX, PCI DSS and HIPAA controls.
Walk through a records request with us.
We'll run a search, place a hold and build the export package, in about 20 minutes.